Runtime security for AI agents

With MiniMako you run fleets of autonomous agents on Linux with full kernel-level security.

Works with
n8n OpenClawOpenClaw PicoClawPicoClaw Cheshire Cat AICheshire Cat AI and any Linux agent

Built for teams running autonomous agentic work on Linux servers

MiniMako is built for AI infrastructure teams, startups building agentic platforms, DevOps and platform teams, security teams that need to know what agents do when they run code on their behalf.

n8n OpenClaw PicoClaw Cheshire Linux
Total control over your autonomous agents

Do you really know what your agents do in production?

Most teams running AI agents in production have no kernel-level telemetry at all. Application logs miss what matters: an agent opening a shell, a connection to an unknown IP, a modified system file.

MiniMako works one layer below your applications. It sees what application logs can't, and that's why an agent can't get around it. When one tries to do something outside the perimeter, it blocks it before it runs, instead of flagging it once the damage is done.

Your agents
Application logs see only the output, not the action
Kernel · MiniMako sees every syscall, network, file, process
How it works

Full runtime visibility, in one command

  • You install it: a single command, no kernel changes.
  • It starts monitoring: eBPF telemetry captures real kernel-level behavior, syscalls, network activity and file operations.
  • You stay in control: events land on a dashboard with a full timeline, forensic detail and real-time alerts.
$curl -sSL install.minimako.com | sh
minimako · runtime guard
root@node>
0
Syscalls monitored today
0 blocked
Threats stopped in the kernel
0 agents
Autonomous agents under control
0 bypass
Successful bypasses

Everything you get

Runtime security, forensic observability and frictionless deployment. On your servers, from the first command.
Block and protect

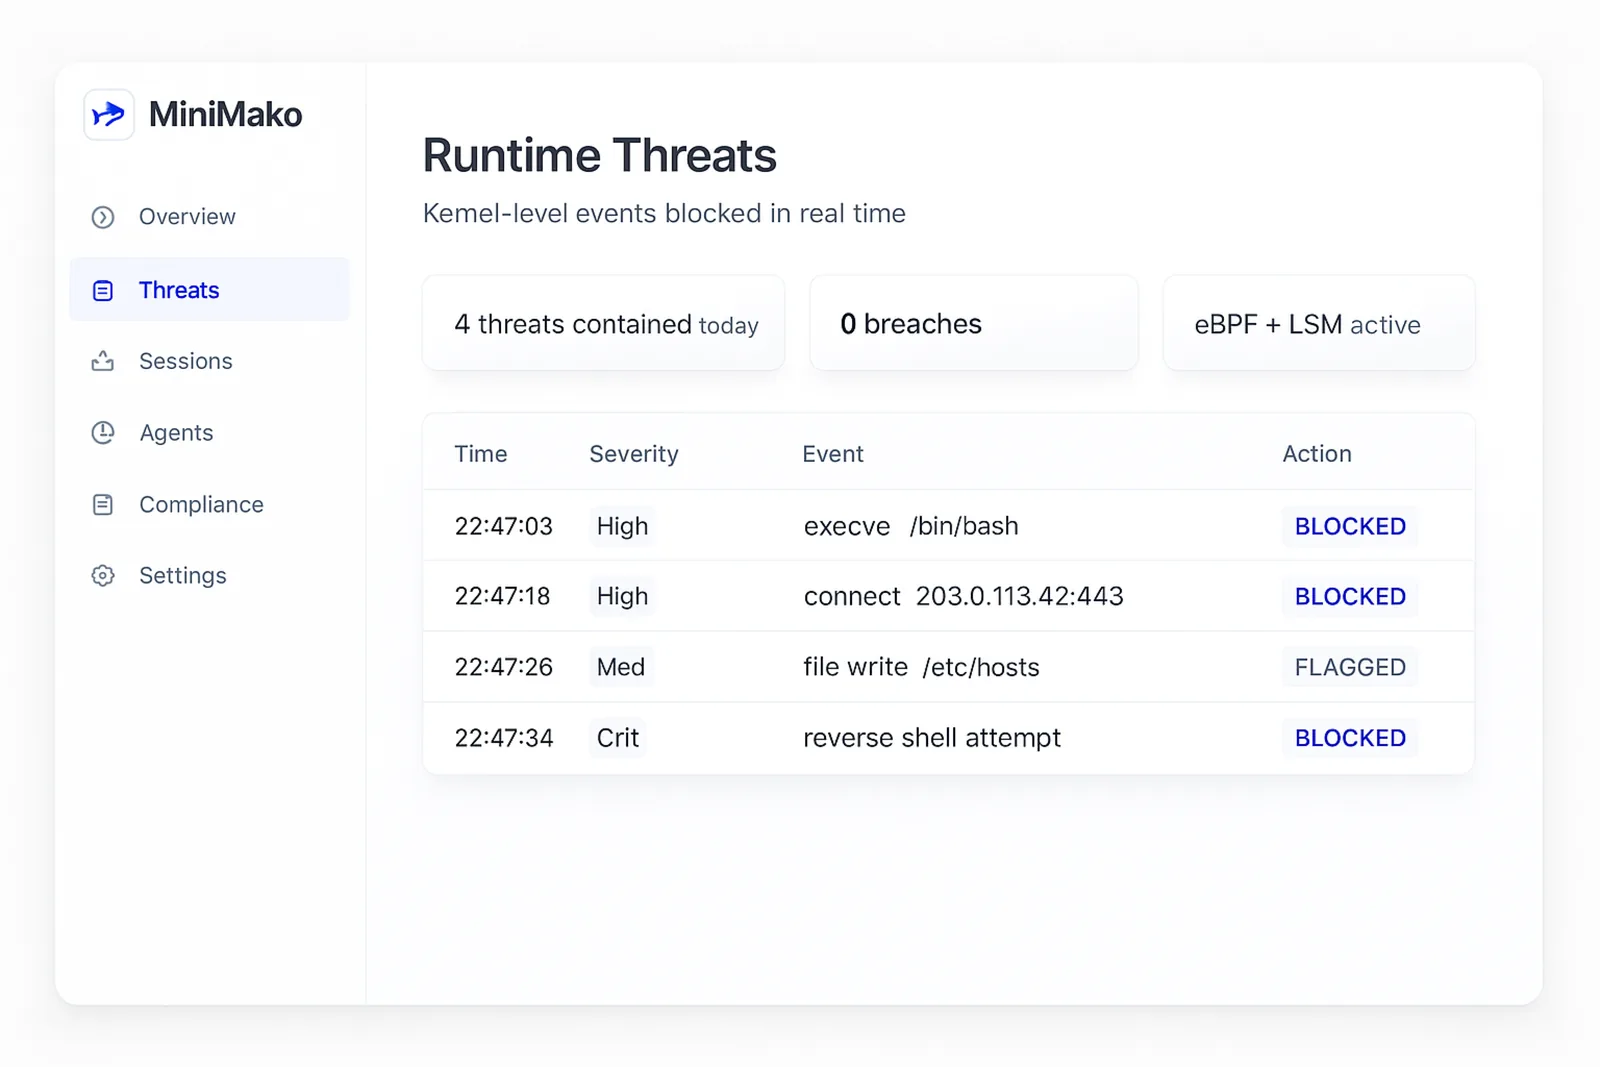
Dangerous actions get stopped inside the kernel

  • Block dangerous actions before they run: miners, reverse shells, sandbox escapes and arbitrary commands stopped the instant they fire, before they cause damage.
  • No agent can disable you: MiniMako runs below the agent stack, so even a compromised agent can't shut it down or get around it.
minimako · threats blocked
MiniMako, threats blocked in the kernel
See everything that happens

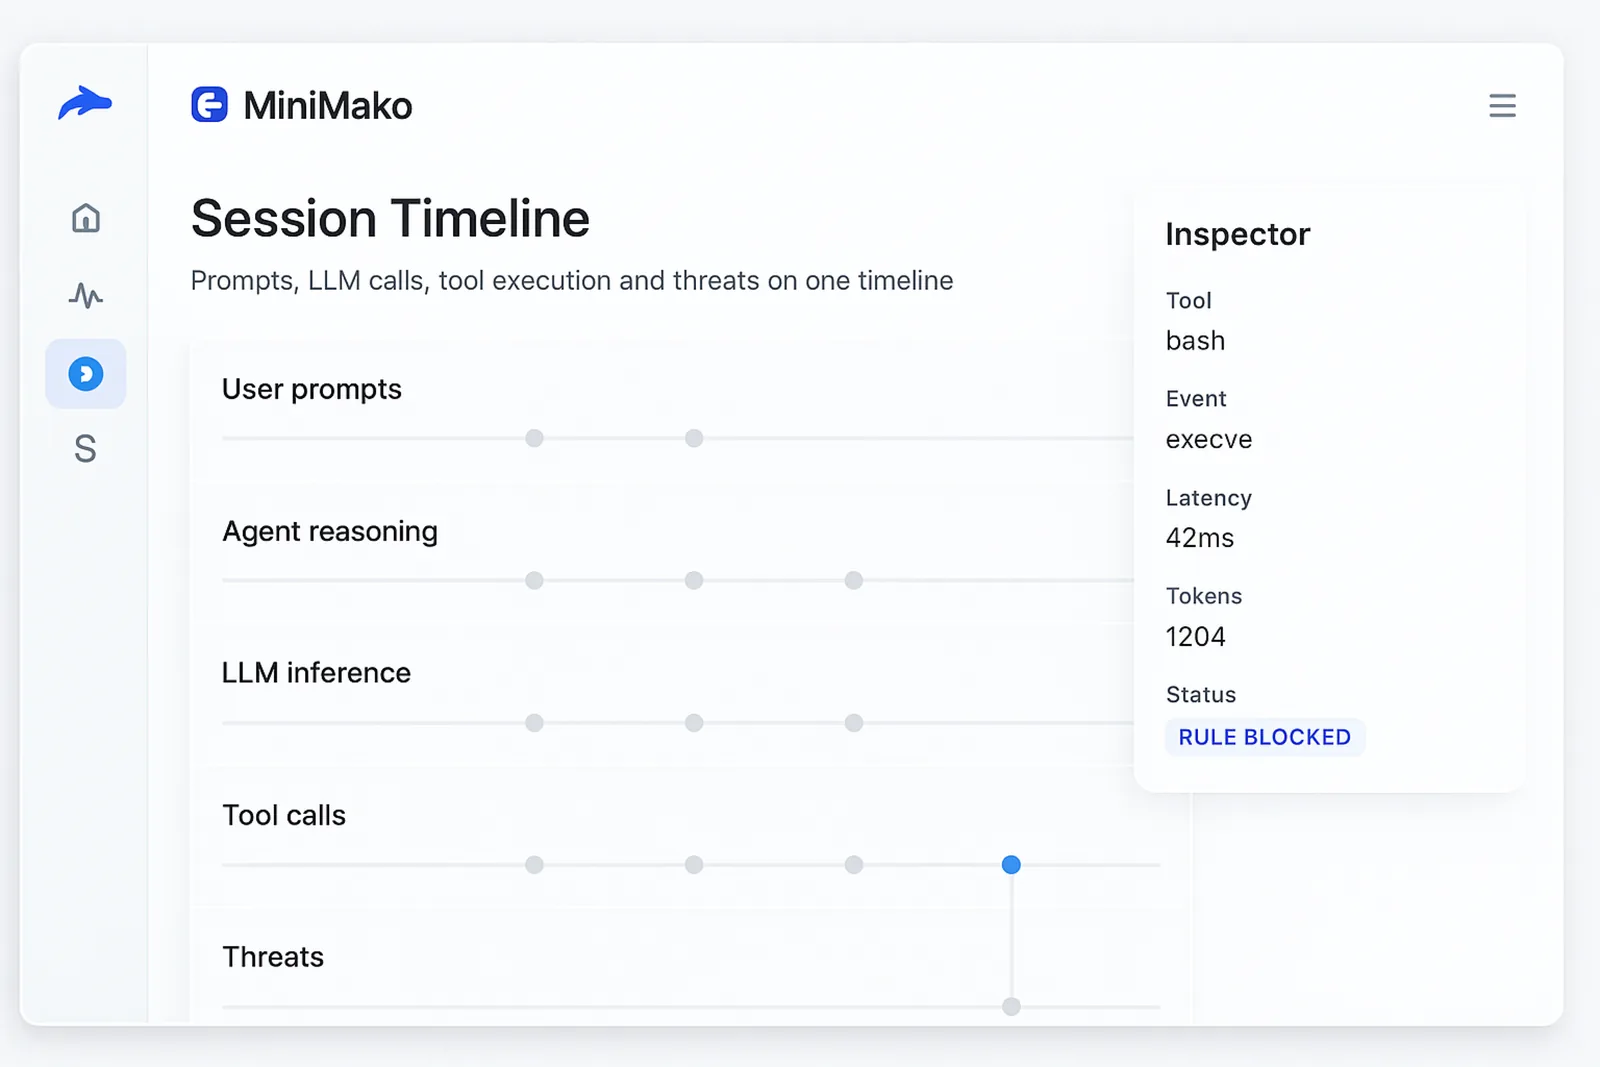
Forensic observability on every agent, in real time

  • See everything your agents do: every syscall, every network connection, every file, every process spawned, where application logs never reach.
  • Reconstruct any incident in seconds: a single timeline correlates prompts, LLM calls, actions and security events, with forensic detail on every node.
  • Govern entire fleets from one console: all the agents running on your servers, correlated in one place.
minimako · runtime timeline
MiniMako, runtime timeline and forensic detail
Compliance and deploy

Audit-ready, without touching your stack

  • You're ready for AI Act, DORA and NIS2 audits: a complete audit trail and runtime observability that satisfy auditors and insurers.
  • Cover any agent: native integrations with the most common ones and support for any custom autonomous agent on Linux.
  • Start with one command: single binary, no kernel changes, telemetry on cloud or self-hosted. Your infrastructure stays as it is.
minimako · deploy & compliance
MiniMako, deploy and compliance
Integrations
n8n OpenClaw PicoClaw Cheshire Cat AI + any Linux agent
Why it pays off

It costs less than a single incident

An agent that wipes a production database can cost you months of work. An AI Act violation runs up to 7% of annual revenue. Sensitive data leaked out is damage money can't buy back.

One incident avoided is enough to start loving MiniMako.

Waitlist

Get in before everyone else.

MiniMako opens soon, to a few. Join the waitlist now and be among the first to give your agents superpowers. Ready?

No spam. Just access, when we open.